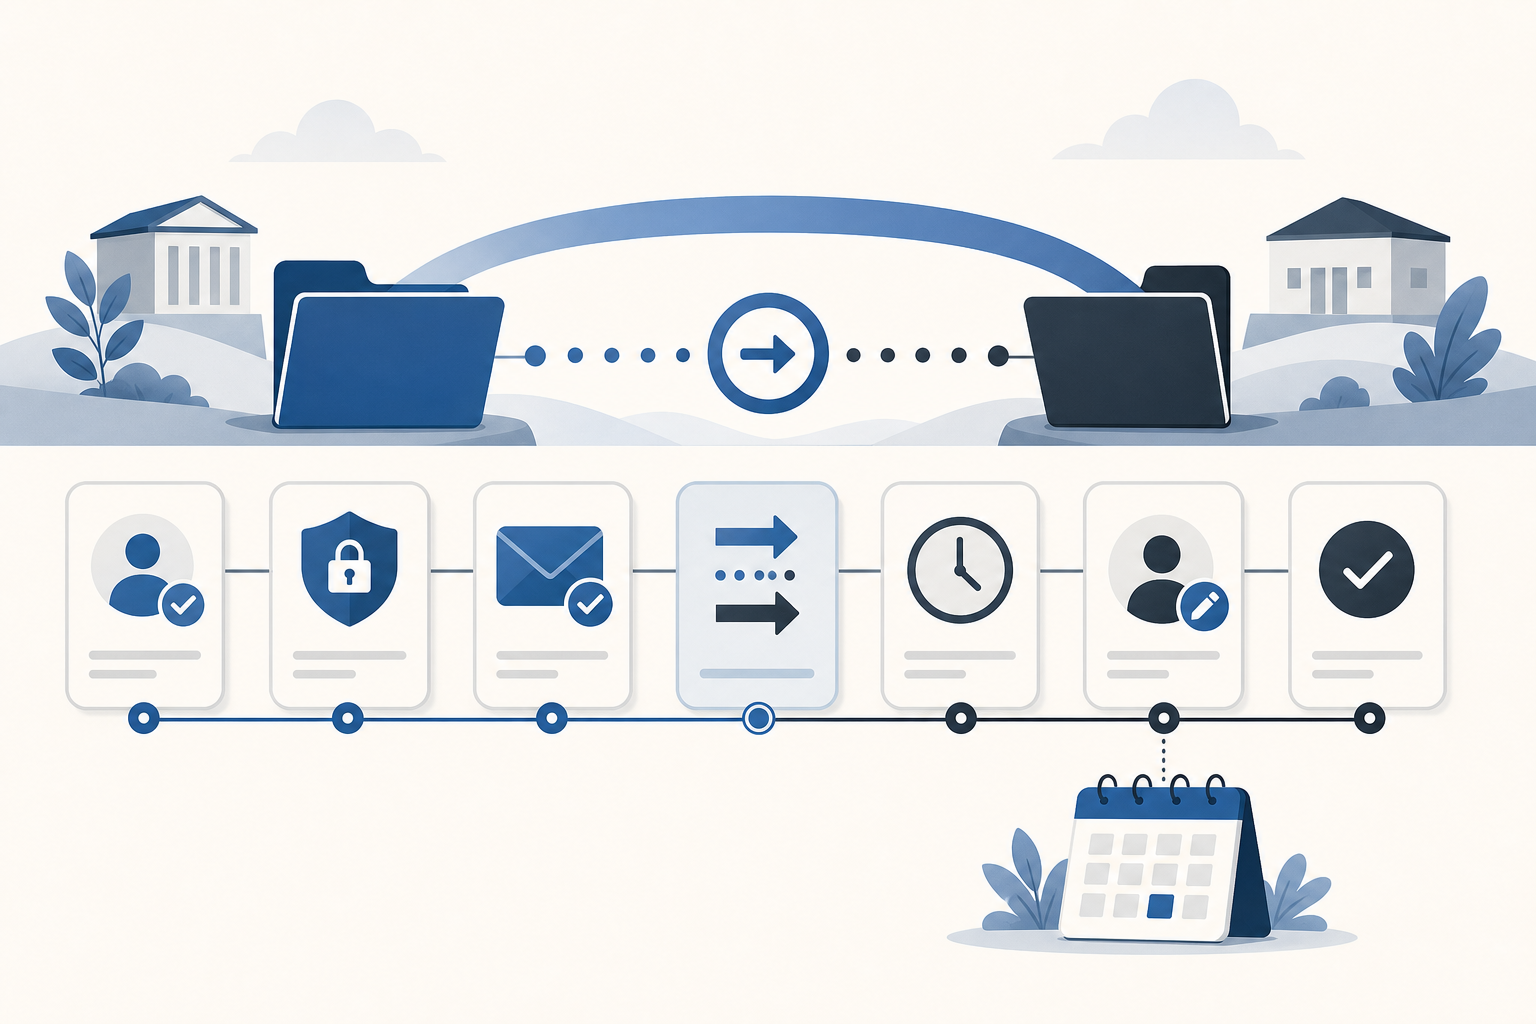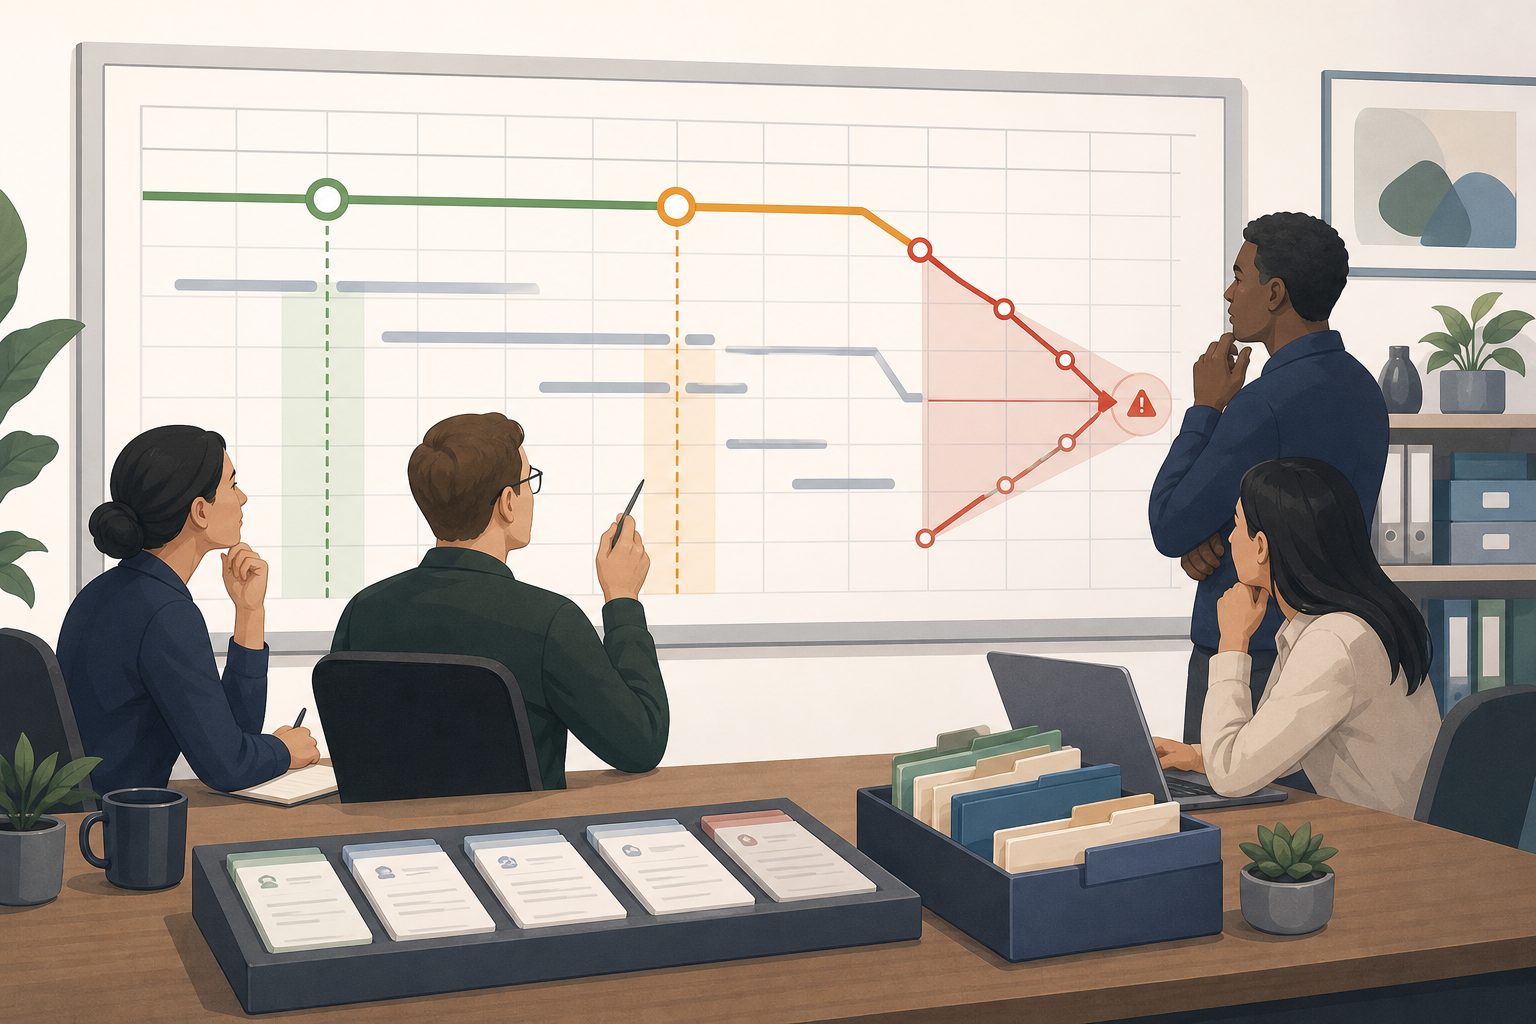
A domain expiration date is often treated as a finish line: renew by that day or deal with the consequences later. That framing creates avoidable risk. Expiration is only one point in a lifecycle that can include registrar-specific late-renewal rules, deletion, registry restoration processes, and final removal. A domain may still be recoverable after expiry, but its website or email may already be affected, costs may change, and the people who can authorize action may be unavailable.
For agencies and IT teams, the practical lesson is simple: routine renewal and recovery are different operating modes. A reliable process does not assume there is a universal grace period. It records the recovery path for critical domains before anyone needs it.
This article shows how to build a recovery-window register: a compact control that sits alongside your renewal inventory and answers the questions that matter when a domain is late.
Why expiration is not a safe recovery deadline
Registrar and registry terminology can make an overdue domain appear less urgent than it is. Teams may hear that a name has a grace period and conclude that it is safe to wait. But the period available to a registrant is governed by the registrar's published policy and the relevant TLD's rules, not by a single industry-wide customer deadline.
For generic TLDs, ICANN requires registrars to disclose their auto-renewal and deletion policies, including the expected timing of deletion for an unrenewed registration. That requirement itself is a useful warning: the post-expiration path depends on the registrar's policy. Read ICANN's Expired Domain Deletion Policy before treating any assumed grace period as a plan.
There are also different clocks in play. A registry process can provide a restoration stage after deletion, while a registrar may suspend services, remove renewal options, or apply its own earlier cutoff according to its policy. ICANN's guidance notes that a deleted gTLD name may enter a 30-day Redemption Grace Period followed by a five-day pending delete stage, but that lifecycle should not be mistaken for a promise that a registrant can renew normally until then. See ICANN's explanation of the Expired Registration Recovery Policy.
TLD rules add another reason not to generalize. AWS Route 53, for example, warns that some registries can delete domains before the displayed expiration date if renewal is not completed early enough, with deadlines that vary by TLD. Its domain renewal documentation is a useful illustration of why teams must verify the specific name rather than rely on folklore.
The recovery-window register: a practical control
A recovery-window register is not a replacement for a domain inventory. It is a short set of additional fields for domains where loss, interruption, or a rushed recovery would be materially harmful. Think of it as an emergency instruction card prepared while the record is healthy.
Use it for primary web and email domains, identity and authentication domains, high-value redirects, active client domains, key product names, and any domain held in an account with uncertain access.
Record these fields for each critical domain
Domain and TLD: Record the exact name, not only a project nickname.
Business-impact tier: For example, critical, important, or standard. State whether interruption affects website traffic, email, authentication, redirects, or another service.
Registrar and account owner: Identify the sponsoring registrar, the account-holding organization, and the internal person or team with access.
Expiration date: This remains the normal scheduling reference, not the final safe action date.
Routine-renewal deadline: Set an internal deadline before expiration, leaving time to resolve billing, approval, or login problems.
Late-renewal policy verified: Link or reference the registrar's current policy and record the date it was checked.
Restoration availability: Record whether restoration may be possible, who must request it, and the source used to verify that information. Do not fill this field with an assumed number of days.
Escalation owner and approval owner: Separate the person who starts incident response from the person authorized to approve an exceptional cost or client charge.
Recovery-policy review date: Policies, account arrangements, and service importance change. A stale recovery note is better than no note only if someone knows it needs rechecking.
The register should record facts and sources, not predictions. “Likely recoverable for 30 days” is weak. “Registrar policy checked on [date]; operations lead contacts registrar support; finance director approves recovery charge” is actionable.
Use two deadlines, not one
The most useful decision framework is to assign two internal deadlines to every critical record.
Routine-renewal deadline: The date by which renewal should be complete under normal conditions. Put this before expiration. It protects time for client approval, an expired payment method, a locked account, or an unclear invoice.
Escalation deadline: The point at which a missed routine renewal stops being an ordinary administrative task and becomes an urgent incident. At that point, the owner confirms current status, checks the registrar's live policy, alerts the approver, and contacts the registrar if needed.
These deadlines change the team's behavior. Instead of asking, “Has it technically expired?” the team asks, “Are we still in routine work, or do we need the recovery path now?” That distinction prevents a late but manageable renewal from drifting until it becomes a restoration or deletion problem.
A five-step workflow for building the register
1. Select domains by impact, not by renewal date alone
Start with the domains that would cause immediate business disruption or reputational harm. Do not let a long expiration date exclude a record. The purpose is preparedness, so a critical domain expiring next year may deserve review before a low-value name expiring next month.
2. Verify the registrar path while the domain is active
Find the registrar's published expiry, deletion, and restoration information for the specific TLD where possible. Confirm the account holder, renewal method, billing owner, and support route. If a reseller is involved, establish who can actually make a request. Record the policy source and verification date.
For a domain that is already overdue, skip debate about generic timelines and contact the sponsoring registrar or reseller immediately. ICANN likewise directs registrants to their registrar or reseller to understand available renewal options in its expired-domain renewal guidance.
3. Pre-approve the human handoffs
A recovery effort often fails through authorization delay rather than technical complexity. Name an escalation owner, a financial approver, and a client contact where relevant. Include an out-of-hours route for the highest-impact domains. The goal is not to create bureaucracy; it is to avoid discovering that the only person able to approve a rescue is on leave.
4. Test one record in a tabletop exercise
Use a hypothetical scenario: an agency discovers on Friday afternoon that client-example.com expired yesterday. The account is owned by a former contractor, the client must approve exceptional spend, and the site receives customer enquiries.
Walk through the record. Can the operator identify the registrar? Can they log in or reach the account owner? Does the entry identify the current policy source? Does it state who contacts the client and who approves the cost? If the answer is no, the register has found a real control gap without waiting for an outage.
5. Review after changes, not only on a calendar
Recheck recovery details when you change registrars, acquire a portfolio, onboard or offboard a client, replace a billing contact, or retire a vendor. These events often change the practical ability to renew more than the expiration date itself.
Common mistakes the register prevents
Confusing registry timing with registrar availability. A registry's lifecycle does not tell you what the registrar will permit a customer to do at a given moment.
Using a single “grace period” column. A single number hides policy differences, TLD variation, and the distinction between ordinary renewal and restoration.
Leaving recovery authority in a notes field. An unstructured note such as “ask Sarah” becomes useless when there are several Sarahs, the client relationship has changed, or the event is urgent.
Only checking a record after expiry. By then, account-access and approval problems have become time-sensitive incidents.
Assuming registrar notices complete the process. ICANN requires certain expiry notices, but notices are sent to the listed registrant contact. They do not establish internal ownership, approval, or coverage.
Make the register maintainable
A spreadsheet for domain renewals can hold the first version of this process, especially for a small portfolio. Keep the register deliberately narrow. If every low-risk parked name needs eight fields and quarterly review, the control will decay. Apply the full recovery fields to critical and important domains, then use ordinary renewal monitoring for the rest.
As the portfolio grows, make the information visible where the team already manages domains across registrars. Tags can identify critical assets, customer context can clarify who authorizes action, and structured fields can keep policy checks from disappearing into ticket comments. The aim is a maintained operational record, not a one-time audit document.
Where domainnotifications.com fits
domainnotifications.com can support the routine side of this workflow by centralizing tenant-owned domain inventories across registrars, tracking renewal dates, and routing reminders through email, Slack, SMS, or webhooks subject to plan entitlements. Teams can use tags, roles, customer organization on paid plans, and CSV/XLSX import and export to keep ownership and portfolio context close to the renewal record. Learn more about domain expiration reminders and domain portfolio management software.
Ultimate workspaces can use custom attributes for fields such as “policy verified date,” “restore approval owner,” and “business-impact tier.” The platform tracks renewals and reminders; it does not register domains or perform automatic renewals. Your team must still verify the specific registrar and TLD policy, retain account access, and act before a recovery window becomes an emergency.