Your Domain Renewal Notices May Be Going to the Wrong People
A domain can have the correct expiration date in an inventory and still be dangerously unmanaged. The failure is often not the date. It is the message path.
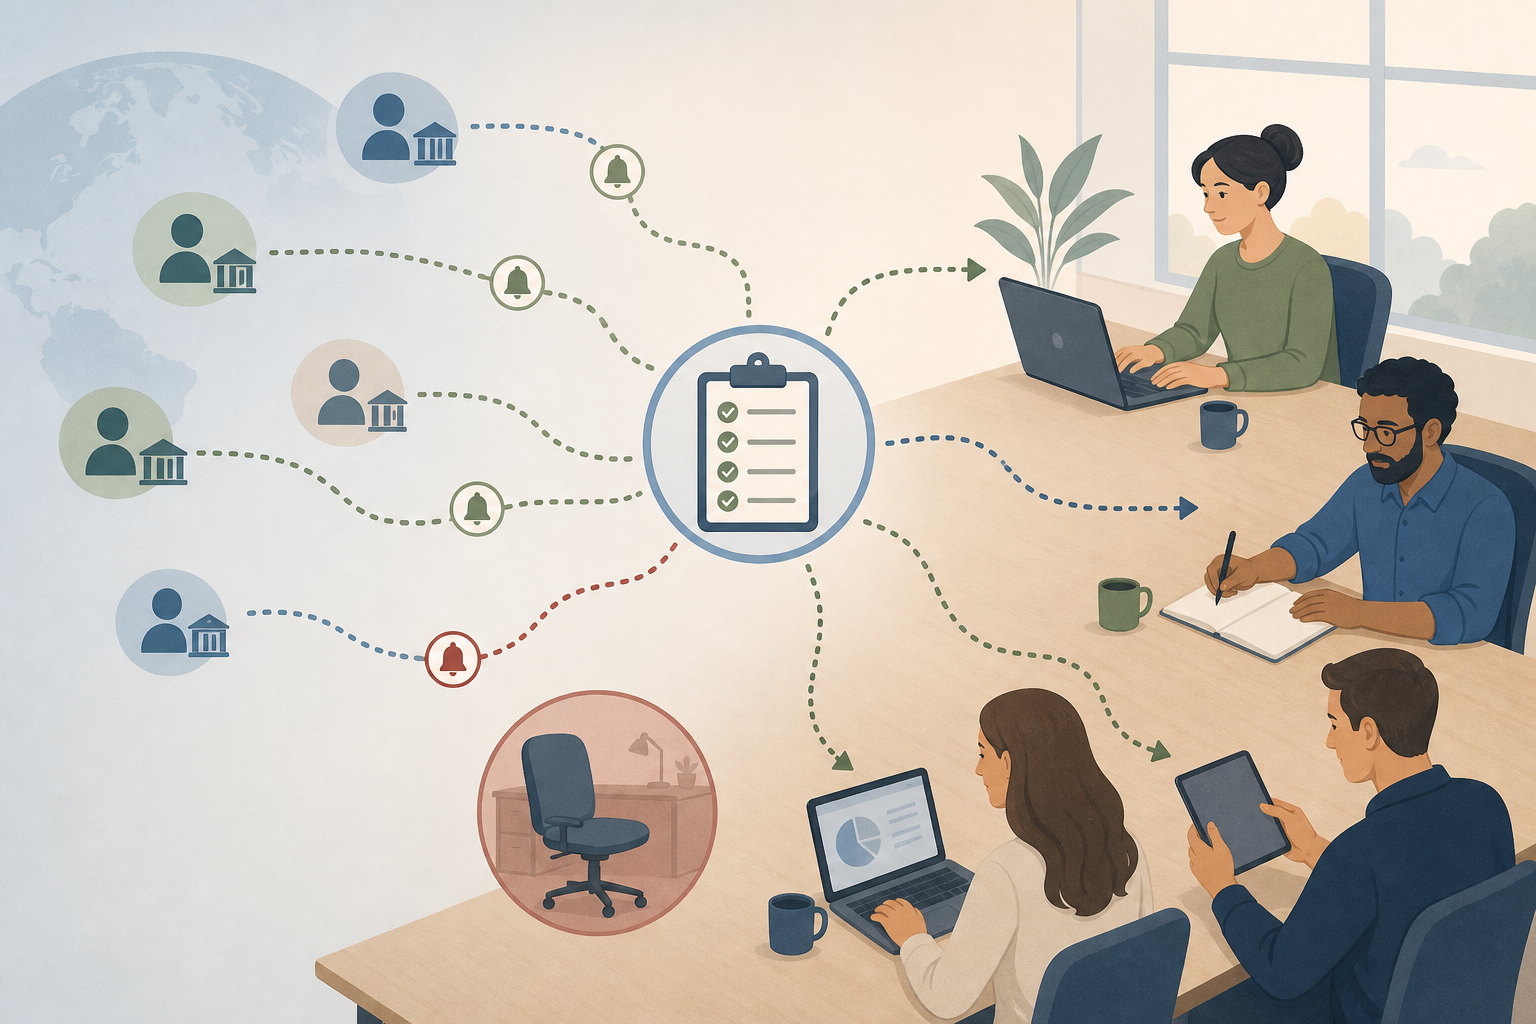
Consider a hypothetical agency responsible for a client's primary website domain. The registrar sends the expiry warning to the former employee who opened the account. The registrant contact is the client's founder, whose personal inbox is rarely checked. The agency's operations team can see the date but cannot approve a charge. Finance can pay but does not know which client should authorize it. Everyone assumes someone else received the notice.
That domain is technically monitored, yet no working renewal process exists.
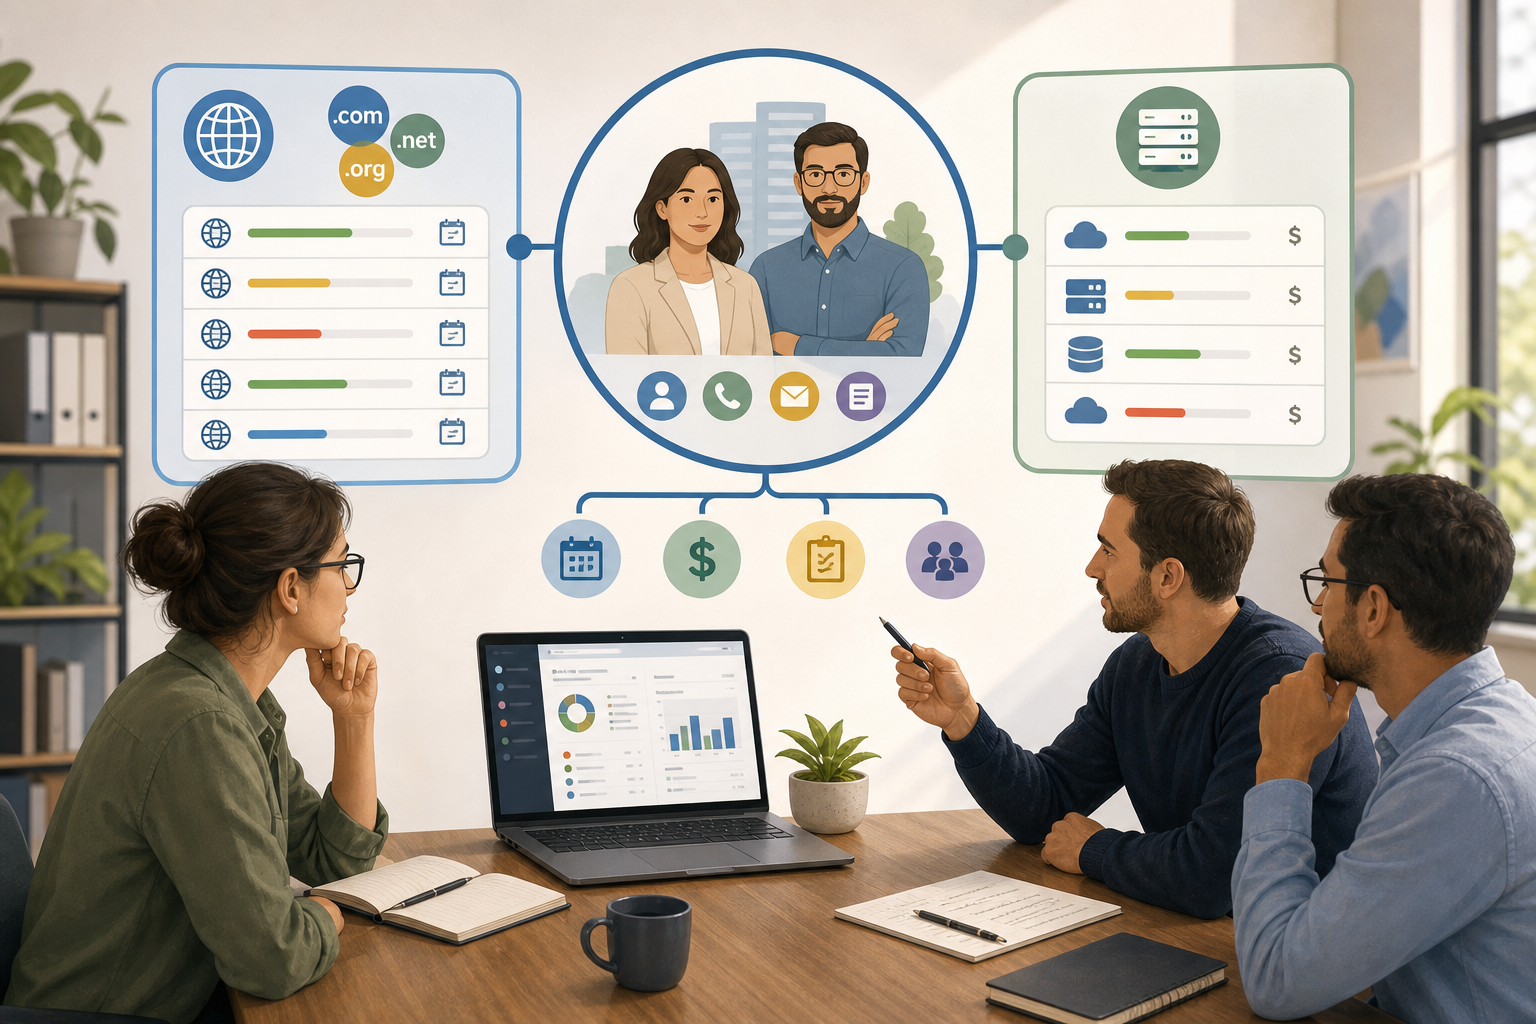
This is a common weakness when teams manage domains across registrars, inherited accounts, client relationships, and staff changes. Registrar emails matter, but they are a safety net, not proof that the right people can make the right decision in time. The remedy is a notification-path audit: a short, repeatable review that connects each important domain's warning messages to an active person, a decision owner, and an escalation route.
Why a registrar email is not a renewal workflow
For applicable gTLD registrations, ICANN's Expired Registration Recovery Policy requires registrars to send pre-expiration renewal notices at about one month and one week before expiry. The policy also describes additional notice requirements in certain post-expiration deletion situations. See ICANN's overview of expiry recovery notices.
Those requirements are useful. They do not answer the operational questions a team must settle:
Which mailbox actually receives each notice?
Is that person still employed, engaged, and reachable?
Can they access the registrar account?
Can they decide whether the domain should renew?
Can they obtain client approval or resolve a failed payment?
A renewal alert delivered to a valid but inactive personal inbox is not a control. Neither is an alert delivered to a capable engineer who has no authority to approve a client expense. Treat notice delivery and renewal ownership as separate things that must be deliberately connected.
Different registrars can notify different contacts
It is risky to assume that every registrar uses the same recipient model. A single domain can have a registrant contact, an account holder, a billing contact, and a platform administrator. Depending on the provider and message type, those people may receive different communications.
For example, Cloudflare documents that some expiry notifications go to a Super Admin while weekly, daily, and post-expiration notices go to the WHOIS registrant contact. Cloudflare's renewal documentation also notes that renewal attempts can fail and eventually require manual action. Namecheap documents that it sends renewal notices to the account's primary email and, when different, the domain registrant email. Read Namecheap's expiration guidance for its stated approach.
Amazon Route 53 says expiration-related messages go to the registrant contact and advises customers to keep that email current. Its domain renewal documentation also makes clear that renewal handling can depend on the TLD and settings.
The practical implication is simple: do not record only “registrar” and “expiration date.” Record where the notices go and whether that path leads to a real outcome.
The five-field notification-path audit
Start with domains whose failure would affect a public site, email, customer login, payment flow, product launch, or high-value brand. Then work through the rest of the portfolio by renewal date and business importance. For each domain, capture these five fields in the operational record.
Registrar and account owner. Name the registrar and identify the organization or person that owns the registrar account. “GoDaddy” or “Cloudflare” alone is not enough; several client, vendor, or legacy accounts may exist at the same provider.
Registrant contact email. Record the address currently designated in the registration data or registrar record. Do not assume it is a shared business address.
Registrar notice recipient. Verify the primary account email, administrator recipient, or any provider-specific destination for expiry and failed-payment messages. This is a verified field, not a guess based on old documentation.
Renewal decision owner. Assign the role or named person who decides “renew,” “do not renew,” or “seek approval.” In an agency, this may be an account manager plus a client approver. In IT, it may be a service owner.
Escalation recipient. Name who takes over if the usual owner is unavailable, payment fails, access is lost, or a deadline is too close.
These fields expose a useful distinction: the person who receives a registrar message may not be the person who can complete the renewal. The audit succeeds only when both sides are known.
Add four fields where risk justifies them
Renewal setting: Record whether automatic renewal is enabled, disabled, or unknown. Do not treat this as a substitute for review.
Billing owner: Identify the party responsible for maintaining the payment method and resolving a rejected charge.
Approval requirement: State whether the client, business owner, legal team, or finance function must approve the spend.
Last path test date: Record when someone last verified recipients, access, and action ownership.
If a domain has an intentional non-renewal decision, record that decision, its owner, and the date. “Do not renew” should be an explicit instruction, not an absence of action that looks like an oversight.
Test the path, not just the contact address
A contact list becomes stale quickly. A notification-path audit should include a small test of how work would move when an alert arrives. This does not mean deliberately letting a critical domain approach expiration. It means reviewing the current registrar settings, a recent genuine notice where available, or the provider's documented recipient behavior.
Ask these questions in order:
Does the identified recipient still control and actively read the mailbox?
Does that recipient know this domain is part of their responsibility?
Can they sign in to the right registrar account, including any required multi-factor authentication process?
Can they approve or initiate renewal, or do they know exactly who can?
Would a failed-payment or post-expiration notice reach the same people, or a different group?
Is there enough lead time to obtain client or internal approval before the provider's actual cutoff?
The last point matters. Expiration handling is not uniform across registrars and TLDs. Namecheap, for example, documents that some TLDs need renewal several days before the stated expiration date. See its guidance for selected country-code domains. Avoid building a process around the assumption that every domain remains renewable under the same conditions until the same deadline.
Use a two-layer reminder design
The most resilient approach has two layers with distinct jobs.
Registrar communications: Keep them enabled and directed to current contacts. They provide provider-specific status, billing failures, verification requests, and account context.
Team-owned renewal reminders: Track the renewal date independently and route reminders to people responsible for the outcome, rather than relying on whichever individual the registrar happens to contact.
This design is particularly useful for agencies. A client may properly remain the registrant and payer, while the agency needs advance visibility to request approval, coordinate the work, and confirm that renewal occurred. It also helps IT teams where the registrant contact must remain a legal or business role but operational follow-up belongs with a service owner.
Be precise about the boundary: reminders surface deadlines and prompt action; they do not renew a domain. The operator must still use the appropriate registrar account, follow the provider's requirements, and confirm the result.
Set review triggers instead of trusting an annual cleanup
An annual portfolio review is valuable, but it will miss changes that break a notification path mid-year. Run a focused audit whenever one of these events occurs:
An employee, contractor, agency, or client contact leaves.
A domain is transferred or a registrar account changes hands.
A client is onboarded, offboarded, acquired, or reorganized.
Billing ownership or the payment method changes.
A domain becomes business-critical because of a launch, migration, or new email use.
A registrar notice bounces, a payment fails, or a reminder reveals unclear ownership.
For the regular cadence, review notification paths before the next concentrated period of renewals, not after notices have already started arriving. Sort the portfolio by expiration date and risk. Resolve domains with unknown contacts, unknown account owners, or no escalation recipient first.
Turn the audit into a short operating routine
A practical domain renewal tracker for IT teams or agencies does not need a long meeting. In a monthly operations review, look at domains due in the next 90 days and label each record as green, amber, or red.
Green: Notification recipient, renewal owner, registrar access, and approval path are verified.
Amber: The domain is likely manageable, but a contact, approval, or access detail needs confirmation.
Red: The recipient is inactive or unknown, the account owner is unclear, payment ownership is unresolved, or nobody has authority to decide.
Work red records first, then amber records. This is more useful than treating every upcoming expiration as equally urgent. A domain expiring later with no reachable account owner can be a larger operational risk than one expiring sooner with a tested renewal path.
Keep the record and the reminder process together
A spreadsheet for domain renewals can capture the five audit fields, but it depends on manual follow-up and can separate dates from the people who need to act. As portfolios and teams grow, keep registrar details, notification-path notes, ownership, and renewal decisions in the same operational record.
domainnotifications.com can provide that shared layer for tenant-owned domain inventories across registrars: it tracks renewals, supports team roles, tags, customer organization on paid plans, and CSV/XLSX import and export. Workspace reminders can be routed through email, Slack, SMS, or webhooks subject to plan entitlements. It does not register domains or perform automatic renewals. For teams building the broader process, see how to build a maintainable domain inventory and how to use Slack domain expiration alerts without creating noise.
The goal is not to replace registrar messages. It is to make sure that, when those messages arrive, a current team knows who owns the decision, who can act, and what happens next.